
Facebook Page Admin Access: Protect Your Account and Organize Team Permissions
A working Facebook Page needs clear permissions and secure administrator accounts. Learn how to diagnose access problems, delegate tasks, manage staff departures, and use official recovery options in markets where Facebook is available.
Personal profiles, Pages, and business tools are different layers
Facebook Page admin access is not simply a password that a team can pass around. A personal account identifies the person signing in, a Page represents the public-facing business or organization, and business management tools help organize access to business assets. Treating these as separate layers makes both delegation and troubleshooting easier.
For example, a colleague may be able to sign in to Facebook but still lack permission to manage your Page. Another person may be able to publish content without having authority to change who controls it. Successful account registration or phone verification does not establish either type of Page permission.
Use individual, authorized accounts rather than making a shared personal profile the team's operating model. If a colleague needs to register an account, follow Facebook's current requirements; do not assume that a new or additional account is necessary to resolve a permissions problem. Meta previously announced work accounts for limited business testing, but that announcement is not evidence that every organization can use them today.
This guidance applies in markets where Facebook is available. Local restrictions, account eligibility, and regional feature availability can affect what your team can do. Business tools and labels can also differ between accounts, so identify the asset and permission involved rather than relying on one universal menu path. *
Diagnose the missing access before changing anything
Start with a precise description of the failure: the administrator cannot sign in, the Page is missing, a specific task is unavailable, or access changed unexpectedly. These are different problems. Record the affected Page, the account being used, the attempted action, and the exact error message, without collecting passwords or verification codes.
If the person can sign in, confirm that they are using the account intended to receive access. Ask an existing authorized administrator to inspect the relevant Page and business access records, where available. Compare the person's assigned permissions with the task they cannot perform, and check whether an invitation is still awaiting acceptance.
If the administrator cannot sign in at all, focus on account recovery rather than repeatedly changing Page permissions. If unfamiliar administrators, unauthorized advertising charges, or unexpected security changes appear, treat the situation as a possible compromise. Avoid making broad changes merely to see whether something works: they can obscure the original issue and give people unnecessary authority. *
Give task access for the job, not full control by default
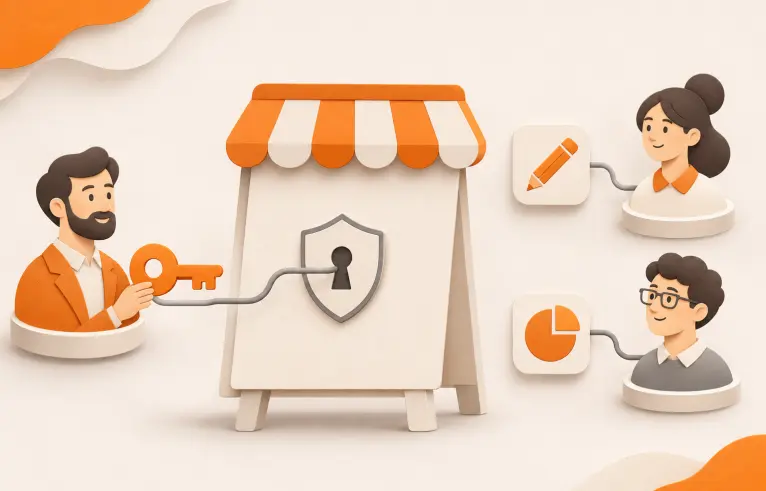
Meta's Page experience distinguishes between broad control and access for particular tasks. Its examples include content, messages and community activity, advertising, and insights. The practical principle is least privilege: assign only the authority someone needs to perform their agreed responsibilities.
Write down the job before choosing permissions. A content contractor may need to prepare and publish posts, while an analyst may only need performance information. Neither responsibility automatically justifies control over other people's access. Reserve broad administrative authority for people who are accountable for managing the business's access arrangements.
Read the permission description shown in your own account before confirming a change. Labels and interfaces evolve, and older descriptions of full or partial control should not be treated as an exact guide to today's buttons. If a permission grants more than the role requires, reconsider the assignment rather than choosing it for convenience.
As a continuity measure, identify an appropriate trusted colleague who can help manage access if the primary administrator becomes unavailable. This is an organizational recommendation, not a universal administrator requirement or number limit. Each person with broader authority should understand the responsibility and have a secure account. *
Protect the administrator's recovery contacts and sign-in methods
An administrator's account security is part of the Page's security. Review the recovery email address and phone number attached to that account, and make sure the account holder can still use them. An obsolete work mailbox or a number controlled by a former employer can become a serious obstacle when verification is required.
Enable two-factor authentication using an option Facebook offers for the account. Meta describes codes from a phone or authenticator app, and also offers passkeys as a sign-in option. Choose methods the account holder can maintain securely over time, and follow the current account interface when reviewing available alternatives.
Use a unique password, review recognized sessions, and enable login alerts where available. Facebook's Security Checkup can help identify account risks. Keep recovery arrangements private: the business needs confidence that access is maintainable, not a spreadsheet containing employees' passwords or authentication codes.
Plan for changes before they happen. When an administrator changes phone, loses a device, or leaves the organization, review their recovery arrangements while they still have legitimate access. Do not assume that receiving a code once means the same number will remain available for a future security challenge. *
Invite a colleague and verify their actual permissions
Before sending an invitation, confirm the intended recipient through a trusted communication channel and agree on the scope of work. Use the access-management options available for the relevant Page or business asset. Check the recipient details and permission summary carefully before submitting the invitation.
Ask the colleague to accept through their own account, then verify the result from both sides. The administrator should review the resulting access entry; the colleague should confirm that the required task is actually available. An invitation being sent is not the same as a completed, usable assignment.
Choose a low-risk check suited to the role, such as viewing the required insights or preparing an unpublished draft where that workflow is available. Do not use a live advertising purchase or unnecessary public post merely as a permissions test. If something is missing, compare the assigned scope with the intended responsibility before expanding access.
Keep a simple internal record of who approved the assignment, what work it covers, and when it should be reviewed. This creates a practical handover reference without making a shared login the team's source of continuity. *
Handle departures and suspicious changes as separate workflows
For a planned departure, complete the work handover before removing permissions. Establish who will take responsibility for pending content, community responses, reporting, and advertising work as applicable. Verify that the remaining authorized people can perform their responsibilities, then remove the departing person's access from the relevant assets and review the resulting records.
Do not assume that removing one Page assignment also addresses every connected business asset or external service. Review the actual access relationships your organization uses. Preserve a record of completed changes, but do not retain the departing employee's personal credentials as a fallback.
An unexpected access change requires a security response instead. Meta has documented malware that targets the personal accounts of people connected to business Pages and advertising accounts. Warning signs can include unfamiliar browser extensions, unauthorized charges, unexpected account activity, or suspicious browser behavior.
Use a trusted device for sensitive recovery work if the usual device may be infected. Remove suspected malicious software, run updated antivirus protection, and follow official account-security guidance. A password reset alone may not prevent renewed compromise when malware remains present; two-factor authentication also does not eliminate every malware risk. *
Use official support with realistic regional expectations
For lost access, open Facebook's official help or recovery options through its app or Help Center. Distinguish a personal-account login problem from a Page access dispute when describing the issue. Have the relevant account and Page details ready, along with a concise timeline of what changed and any genuine security notices.
Meta has introduced a centralized support hub and adaptive recovery processes. Available checks can vary with the situation, and an optional selfie video is among the recovery methods Meta describes. Follow the options offered to your account rather than assuming that another person's recovery sequence will appear for you.
Regional availability matters. Meta's March 2026 update places the AI support assistant in countries and territories where Meta AI is available. Assistance specifically for people unable to log in began with selected cases in the United States and Canada. Neither announcement means that every country, account, or Page access problem receives the same assistance.
Be wary of unsolicited people claiming they can restore ownership for payment or by receiving your security codes. No outside SMS service can grant Page permissions or override Meta's recovery decisions. Official support may provide a route forward, but the outcome depends on the account, evidence, and options available. *
Phone verification is separate from Page authorization
A phone verification request concerns a particular account check; it is not a transfer of Page authority. Before obtaining a number, determine whether Facebook is asking for registration verification, a login challenge, or a recovery step. Solving the wrong problem can leave the original access issue untouched.
For an administrator account that must remain recoverable, prioritize contact methods the account holder can maintain. A temporary SMS number should not be treated as a permanent recovery contact, proof of business ownership, or a way around account restrictions. Number acceptance and later verification requirements can vary, so receiving one message does not guarantee registration or ongoing access.
For the Facebook SMS service listing, visit https://grizzlysms.com/facebook. For additional reading about registration choices, see https://grizzlysms.com/blog/facebook-without-phone-number-what-are-your-options. Assess any SMS option against the specific verification request and your long-term recovery needs, not as a replacement for proper Page permissions. *
FAQ
Does our team need a shared Facebook profile? No. Use individual authorized accounts and assign the permissions each person needs.
How does task access differ from full control? Task access limits work to assigned activities, while broader control carries wider authority. Read the current permission description before granting it.
What should we check before an SMM employee leaves? Confirm the handover, test the remaining team's access, and review the departing person's permissions across relevant assets.
Where should we go after losing access? Use Facebook's official recovery and support options. Available methods, including AI assistance, depend on the account and region. *
Short team-access checklist
Identify the affected account and Page.
Match permissions to responsibilities.
Confirm the invitation recipient.
Test the assigned task safely.
Review recovery contacts.
Enable two-factor authentication.
Record the handover owner.
Remove obsolete access.
Investigate unfamiliar security changes. *